- Solutions
- ISO 27001 compliance
Key management and access control for ISO27001
ISO 27001 compliant processes
Since our first ISO 27001 certification in August 2020, many processes have been supported with ecos’ own products. The entire ecos concept is geared towards electronically supporting internal processes, managing equipment and securing access to rooms and buildings.
ecos – electronically controlled organisation systems
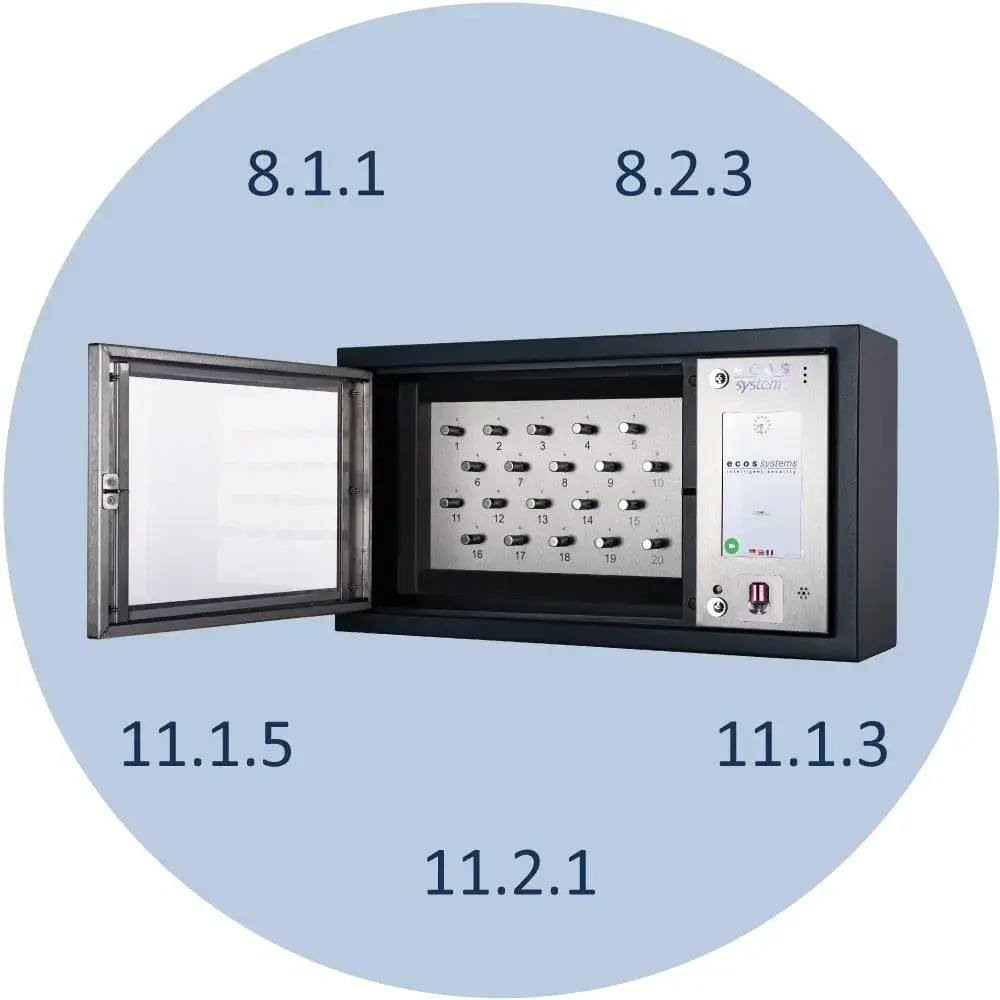
The following ISO/IEC 27001:2022 Annex A controls can be easily met via ecos products:
Organizational controls
A 5.9 Inventory of information and other associated assets
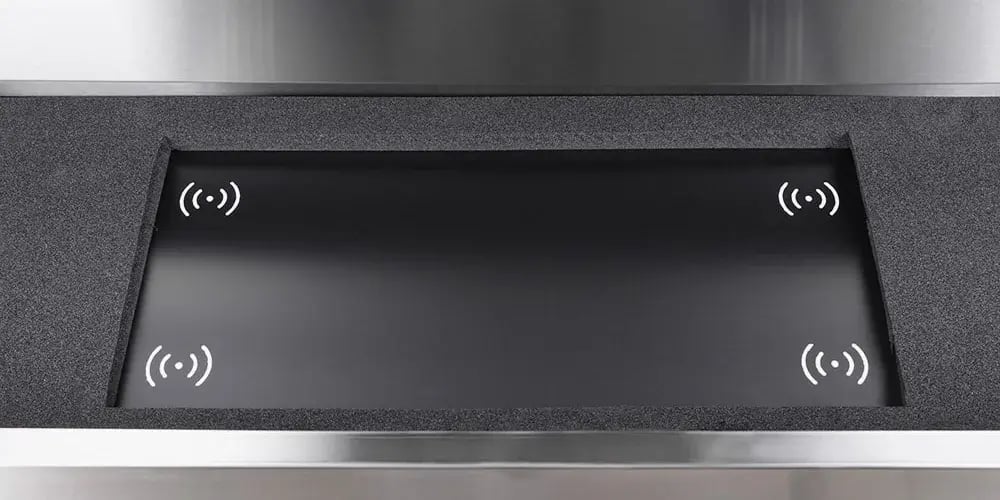
Both in key cabinets and in electronic locker systems, you can use RFID labels and ID recognition to identify their values beyond doubt and log their whereabouts. Even stored items can be recognised and counted in a compartment system with weight recognition.
At any time you have an overview of your values and can take an inventory list with classification in webman2.
A 5.10 Acceptable use of information and other associated assets
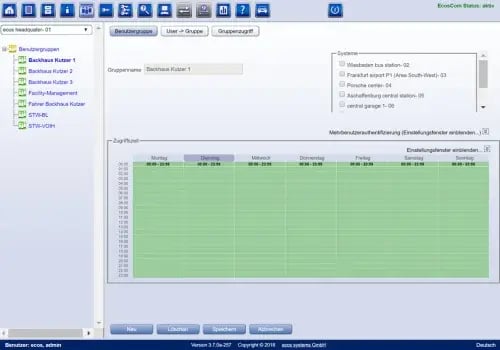
In our webman2 software, you can implement the defined access restrictions per classification level via person or group authorisations. In addition, you can easily check afterwards via an overview which recipient has been assigned which values.
Physical controls
A 7.2 Physical entry
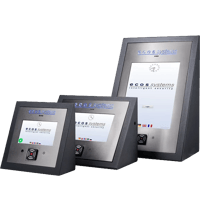
Access to the defined security perimeters required in A 7.2 can be ensured and controlled via our terminals. In the process, login and logout of both authorised persons and visitors are logged and controlled. Visitors must provide their email address for identification and follow your company’s sign-in process. This may include signing a confidentiality agreement, watching a security video, receiving a visitor badge or handing over their personal belongings.
Access points such as delivery and loading areas can also be easily monitored and protected via our compact terminals. These only allow access to identified and authorised persons – whether employees, visitors or delivery personnel.
A 7.3 Securing offices, rooms and facilities
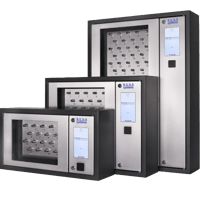
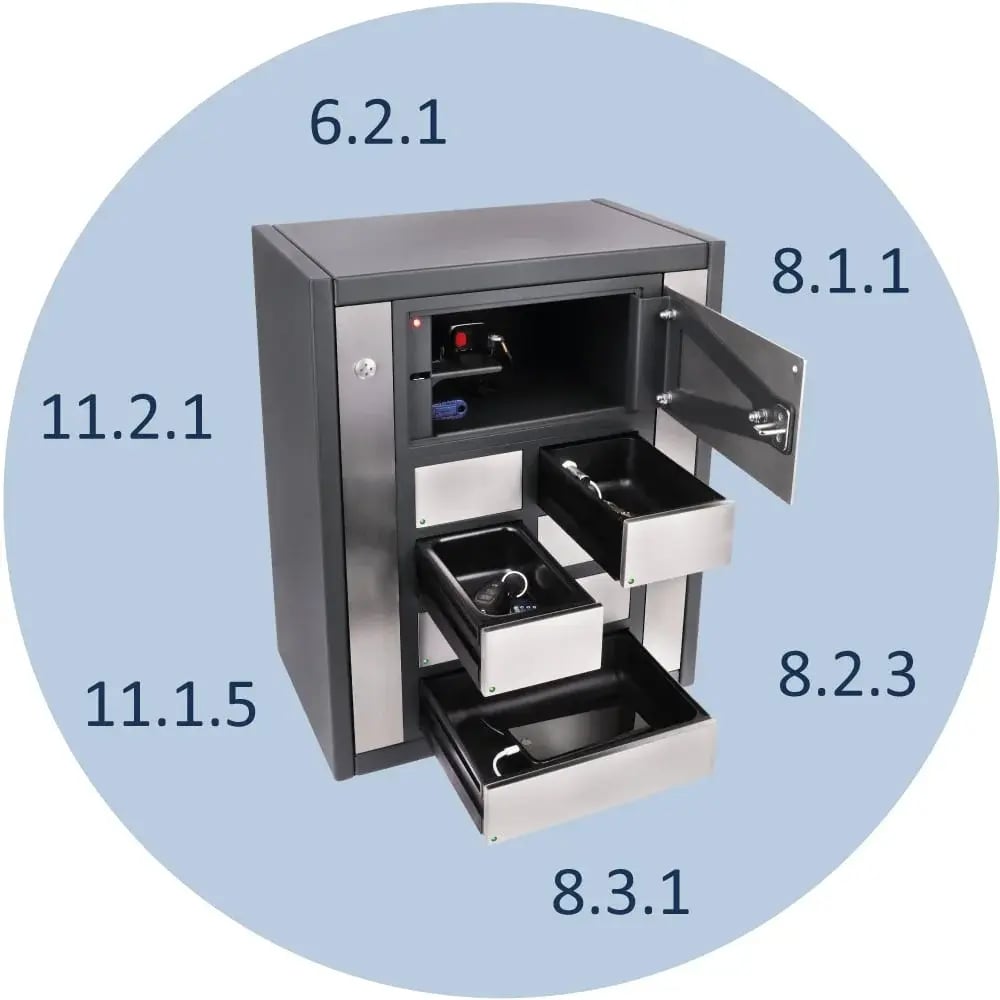
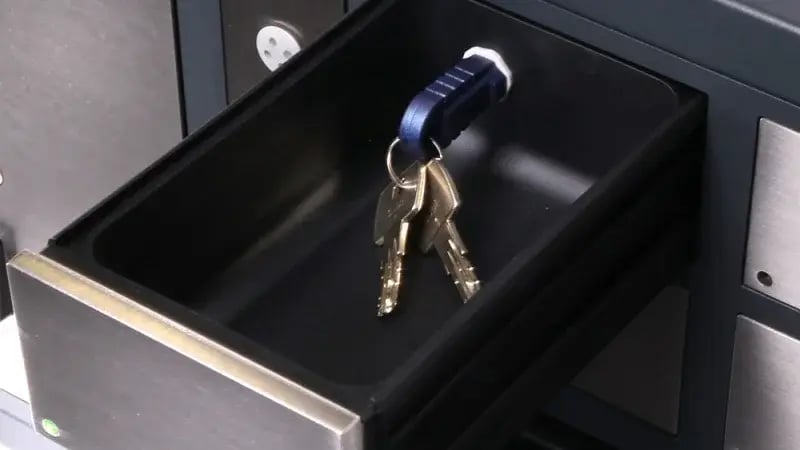
Room keys can be managed in our key cabinets and thus each removal and return can be logged with the associated person. Due to the special protection requirements of archive and server rooms, these keys can also be managed in separate small ecos drawer m/4.
A 7.6 Working in secure areas
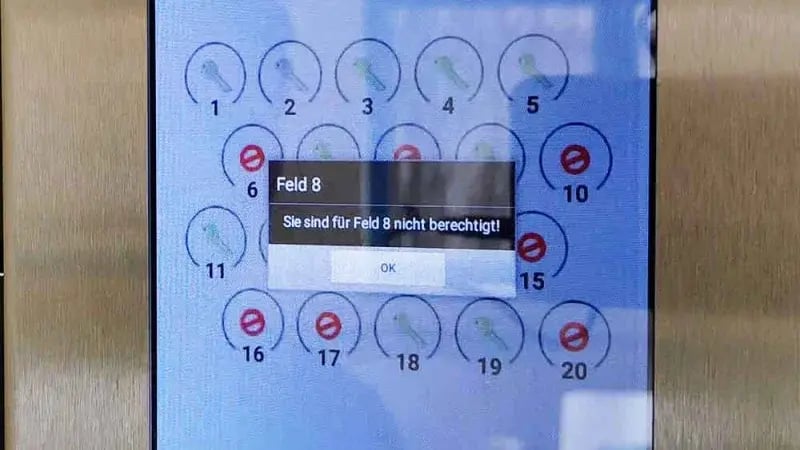
The requirement that employees are only informed of the existence of a secure area when necessary is also covered by the ecos products. On the system, users can only view what has been released for them according to the “need to know” principle.
A 7.8 Equipment siting and protection
Our electronic key cabinets and lockers help protect equipment and resources by preventing unauthorised access and reducing the risk of potential threats such as theft or vandalism.
A 7.10 Storage media
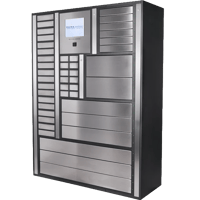
All types of data media, such as backups, hard drives or USB sticks can be stored in our ecos drawer and ecos depots in a controlled manner. Access to highly sensitive information can also be controlled via multifactor/user authentication.
Technological controls
A 8.1 User endpoint devices
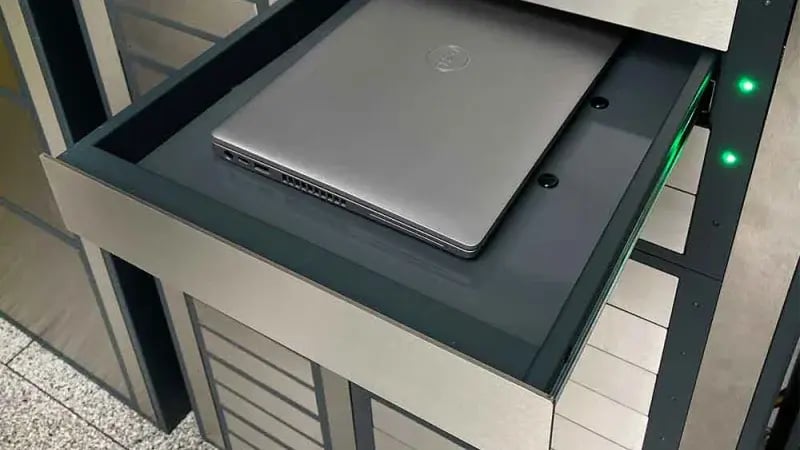
Your sensitive business information can be protected with our lockers. Visitors must hand in their mobile devices or USB sticks in an assigned compartment before entering their premises. This protects you from information theft through unauthorised photos or via USB. In addition, information security is increased by making it impossible to introduce malware. This measure can additionally be required for employees without sufficient security clearance.
Do you need support in implementing your ISO 27001 certification? We are happy to help you!