Google Identity Platform provides the sign-in service that many organizations use to control access to their applications. The ecos integration keeps things simple: your people sign in to ecos with the Google account they already have, and their access follows their Google account as they join, change roles or leave — so there is one less password to remember and no orphaned access left behind.
GENERAL INTEGRATION
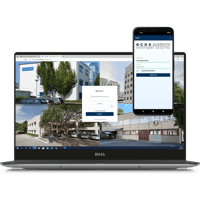
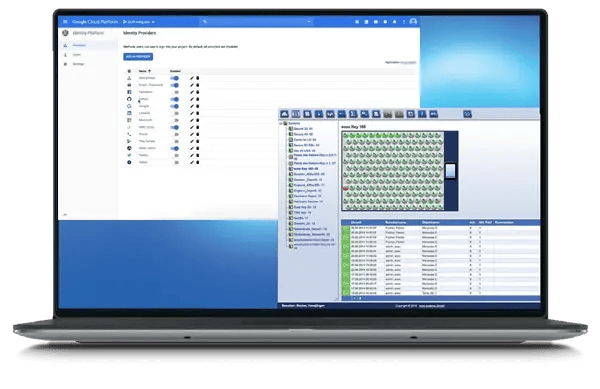
ecos uses Google Identity Platform for single sign-on. Rather than maintaining a separate synced user list, access to ecos is tied to each person's Google account, so authentication and account lifecycle are handled by the identity service your organization already trusts.
How it works
Connect ecos to your Google Identity Platform for single sign-on, entering the connection details Google requires.
Access follows the Google account: it is available when someone joins, adjusts if their role changes, and ends automatically when their account is suspended or removed.
From then on, they use the same Microsoft login, and access ends automatically when their Entra ID account is disabled.
Key Features
Single sign-on with Google
Staff sign in to ecos using the Google account they already use every day, so there is no extra password to issue, remember or reset.
Automatic joiner-mover-leaver access
Because access is tied to the Google account, it is granted when a person joins, follows them as their role changes, and is revoked the moment their account is disabled — with no manual clean-up.
Lightweight by design
This is a sign-on integration, not a data sync: ecos does not import or store a separate copy of your directory. Access is governed entirely by the Google login, keeping setup and maintenance minimal.
One Google login for your team — including ecos.
Give your people single sign-on to ecos with their existing Google credentials and let access follow their Google account automatically as they join, move or leave.