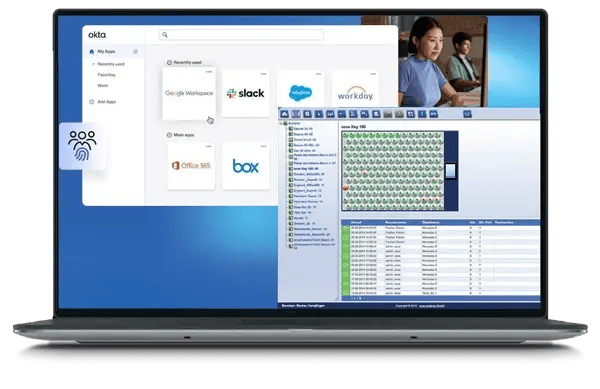
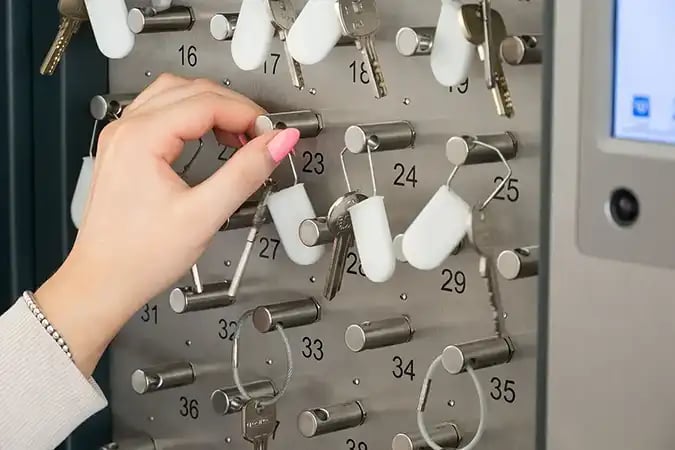
Okta is a leading independent identity provider that organizations use to manage user access across all of their applications from one place. Connecting ecos to Okta extends that control to the physical world, so the same identities and groups that govern your software also decide who can open your key cabinets and lockers.
GENERAL INTEGRATION
ecos synchronizes with Okta through its identity and provisioning APIs. Users and their group assignments are read from Okta into ecos webman, together with the details that identify each person — name, e-mail and department — so your key and asset access is governed by the identity platform you already trust.
How it works
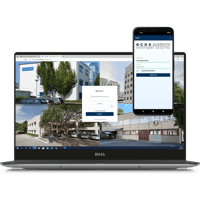
Connect ecos webman to your Okta org, authorizing the integration and entering the connection details Okta requires.
Bring your Okta groups into ecos, where they are mirrored as user groups, so your Okta structure sets access rather than a hand-built list.
ecos provisions and updates users automatically as Okta assignments change, keeping access current.
Operators use single sign-on with their Okta credentials, and access is removed automatically when a user is deactivated.
Key Features
Provisioning from Okta
Users are created in ecos directly from Okta, with name, e-mail and department included, so onboarding for key and asset access needs no manual setup.
Real-time joiner-mover-leaver updates
As people are added, reassigned or deactivated in Okta, ecos updates their access accordingly, so no rights are left in place after they should end.
Seamless single sign-on
Administrators and operators sign in with their Okta credentials, keeping authentication unified across your applications and your ecos products.
One identity platform, extended to keys and assets.
Provision users from Okta, map access to your Okta groups, and enable single sign-on — so physical key and asset access follows the same identities as everything else.